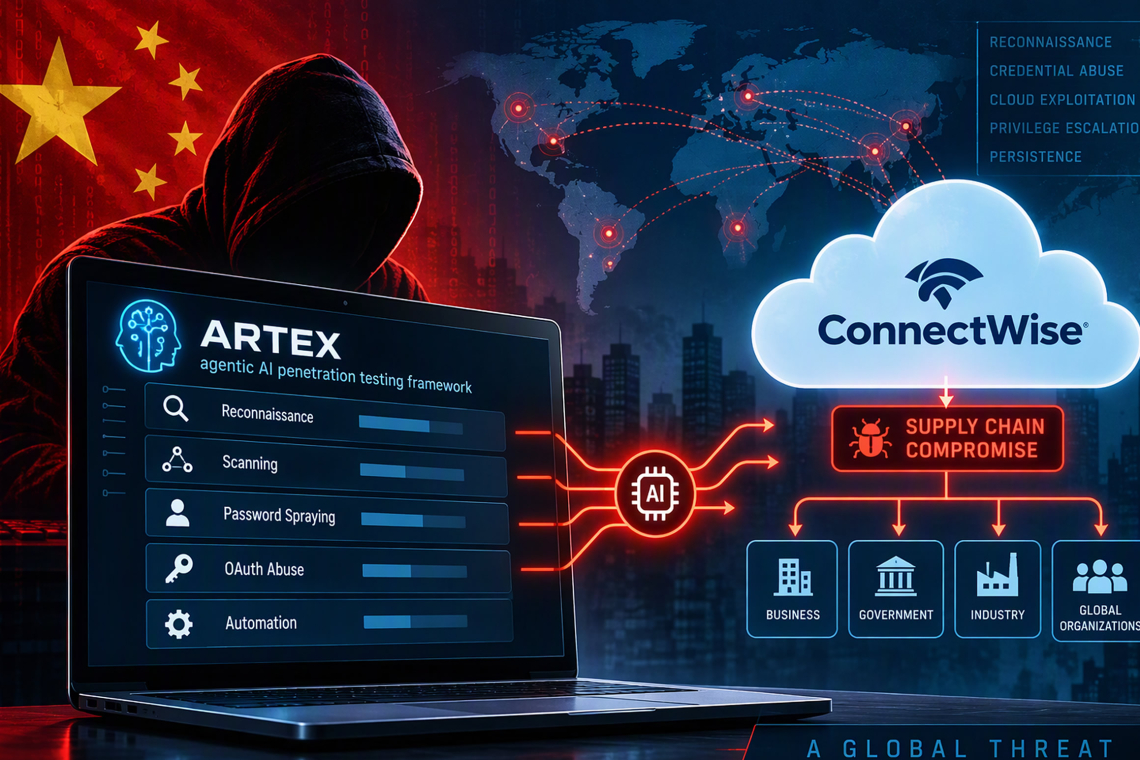
Microsoft has revealed that the recent compromise of ConnectWise Cloud Backup was carried out by Storm-0940, a China-aligned threat actor that increasingly relies on artificial intelligence to accelerate cyber operations. The campaign highlights a new phase in cyber espionage where autonomous AI-driven tools are being used to automate attacks at unprecedented speed and scale.
At the center of the operation was ARTEX, a Go-based agentic AI penetration-testing framework that was originally developed for offensive security research. Although the framework was later taken private following reports of its misuse in attacks against South Korean financial institutions, Storm-0940 successfully weaponized it to streamline reconnaissance, password-spraying campaigns, cloud identity abuse, and privilege escalation activities across downstream victims.
AI-Powered Attacks Executed at Machine Speed
According to Microsoft, Storm-0940 used ARTEX to automate large portions of the attack lifecycle, enabling the group to target hundreds of organizations worldwide since September 2026.
Victims span numerous critical sectors, including:
- Aerospace and defense
- Automotive
- Chemical manufacturing
- Energy
- Financial services
- Government agencies
- Legal services
- Manufacturing
- Media organizations
- Military entities
- Semiconductor companies
- Software vendors
- Technology firms
- Think tanks and nonprofit organizations
Microsoft noted that ARTEX enabled the attackers to operate at "machine speed," allowing them to authenticate to victim environments through previously trusted applications without requiring direct user interaction.

Once access was established, AI-driven automation handled many of the follow-on activities typically performed manually by attackers, including:
- Environment reconnaissance
- Credential manipulation
- OAuth application abuse
- Privilege modifications
- Persistence establishment
- Cloud identity management
This significantly reduced the time required to move from initial compromise to privileged cloud access.
Storm-0940's Established Track Record
Storm-0940 is not a new operation. Microsoft first publicly documented the group in late 2024, linking it to highly evasive password-spraying campaigns powered by the Quad7 botnet, also known as CovertNetwork-1658.
Security researchers believe the actor has been active since at least 2021.
Historically, the group has focused on exploiting internet-facing systems to gain initial entry before using compromised accounts to move laterally across victim environments. The hackers have also demonstrated a strong emphasis on cloud persistence by inserting additional credentials into trusted OAuth applications, enabling long-term access to Microsoft 365 environments.
Compromise Escalated Within Hours
Microsoft reported that several ARTEX-assisted intrusions progressed from initial targeting to privileged cloud access in less than three hours.
The ConnectWise incident demonstrated just how quickly AI-enhanced operations can overwhelm defenders.
Before obtaining application credentials, Storm-0940 relied heavily on automated password-spraying attacks. Microsoft observed ARTEX attempting authentication against more than 2,250 Microsoft 365 tenants, generating approximately 2,900 login attempts per minute.
Between October 10 and October 14, 2026, infrastructure linked to the threat actor conducted attacks against 327 accounts across eight organizations in an effort to compromise Microsoft 365 and Exchange Online environments.
During that period:
- More than 151,000 failed authentication attempts were recorded.
- October 11 marked the peak activity period.
- Attack rates surpassed 2,900 failed logins per minute.
- More than 111,000 failed attempts occurred in a single day.
- Forty-eight accounts experienced over 1,000 failed login attempts each.
Despite the volume of activity, Microsoft reported that none of these password-spraying efforts successfully authenticated, generated tokens, accessed Microsoft Graph, or modified cloud directories.
Attack Shifted After ConnectWise Application Credentials Were Compromised
The situation changed dramatically on October 15, 2026, when Storm-0940 gained access to the identities and credentials of multiple ConnectWise cloud applications.
After securing those credentials, the attackers no longer needed to rely on password-guessing attacks. Instead, the AI agents leveraged the pre-existing trust relationships those applications already had within customer environments.

By abusing legitimate application identities, the threat actors were able to authenticate directly into customer tenants using authorized channels that appeared trusted to the target environments.
This approach allowed the attackers to bypass many traditional detection mechanisms and move deeper into victim networks.
AI Agents Performed Advanced Cloud Operations
Microsoft stated that in several affected environments the AI agents moved beyond simple authentication and executed a variety of administrative operations.
Observed activities included:
- Tenant discovery and reconnaissance
- Microsoft Graph abuse
- Directory enumeration
- Application credential modifications
- Identity and group management changes
- Privileged role manipulation
- Persistence establishment within cloud environments
One of the most concerning findings involved modifications to application credentials. By altering or adding credentials to trusted applications, Storm-0940 could maintain access even after the original compromised application was remediated.
Such persistence mechanisms can create long-term cloud backdoors that survive standard incident-response efforts.
ARTEX Abuse Extends Beyond ConnectWise
Microsoft emphasized that Storm-0940 is not the only threat actor utilizing ARTEX.
Researchers have observed multiple cybercriminal and state-aligned groups across different regions adopting the framework as part of their offensive toolkits.
Separate investigations by Recorded Future's Insikt Group linked another ARTEX-enabled campaign to a Chinese-speaking threat cluster known as TAG-217.
Researchers traced TAG-217 activity back to August 2026, when the group began testing infrastructure intended to support remote access operations and large-scale internet scanning.
Subsequent analysis revealed the threat actor developing additional capabilities targeting:
- Cryptocurrency mining platforms based on YiiMP
- iPhone security testing environments
- Android operating system modification projects
Global Targeting Discovered
Additional research conducted by Zscaler's ThreatLabz indicates that ARTEX-enabled operations were not limited to South Korea.
Investigators found evidence suggesting opportunistic targeting across multiple countries and industry sectors worldwide.
Analysis of a customized ARTEX deployment uncovered:
- AI-assistant configurations
- Automation scripts
- Network-routing utilities
- Synchronization tools
- Prompt histories from Claude Code
- Multi-model AI orchestration workflows
Researchers discovered that ARTEX had been configured to work with several AI models, including:
- DeepSeek
- GLM
- Grok
The framework reportedly directed different AI models to investigate specific tasks and review each other's findings, creating a collaborative AI workflow designed to improve operational efficiency and accuracy.
Evidence Suggests Financial Motives
Prompt-history analysis uncovered requests involving:
- Large-scale collection of personal information
- Bulk transaction records
- Payment gateway API keys
- NFT-related workflows
- Administrative privilege escalation
- Potential monetization of stolen information
These prompts suggest that at least some ARTEX-driven campaigns may have been financially motivated rather than purely espionage-focused.
AI Is Reshaping Cyber Operations
The incident demonstrates how agentic AI systems are becoming integral components of modern cyberattack frameworks.
Unlike human operators, AI agents can:
- Operate continuously around the clock
- Execute multiple attack paths simultaneously
- Analyze large datasets instantly
- Adapt investigations in real time
- Reduce time-to-compromise dramatically
The ConnectWise breach illustrates how AI-assisted attackers can move from reconnaissance to cloud compromise within hours, shrinking defenders' response windows and increasing the potential impact of software supply-chain attacks.
ConnectWise Response
ConnectWise acknowledged that the campaign extends beyond any single vendor and reflects a broader trend of nation-state actors targeting trusted software providers as entry points to larger ecosystems.
The company noted that managed service providers (MSPs) are increasingly attractive targets because a successful compromise can provide access not only to the provider itself but also to numerous customer environments.
Following the attack, ConnectWise temporarily suspended portions of its services and has since been restoring systems in phases. The company indicated that full recovery is expected to take several days as remediation and security validation efforts continue.
The incident serves as a stark reminder that the combination of trusted software supply chains and autonomous AI-powered attack frameworks is creating a rapidly evolving threat landscape, one where adversaries can scale sophisticated operations faster than ever before.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
