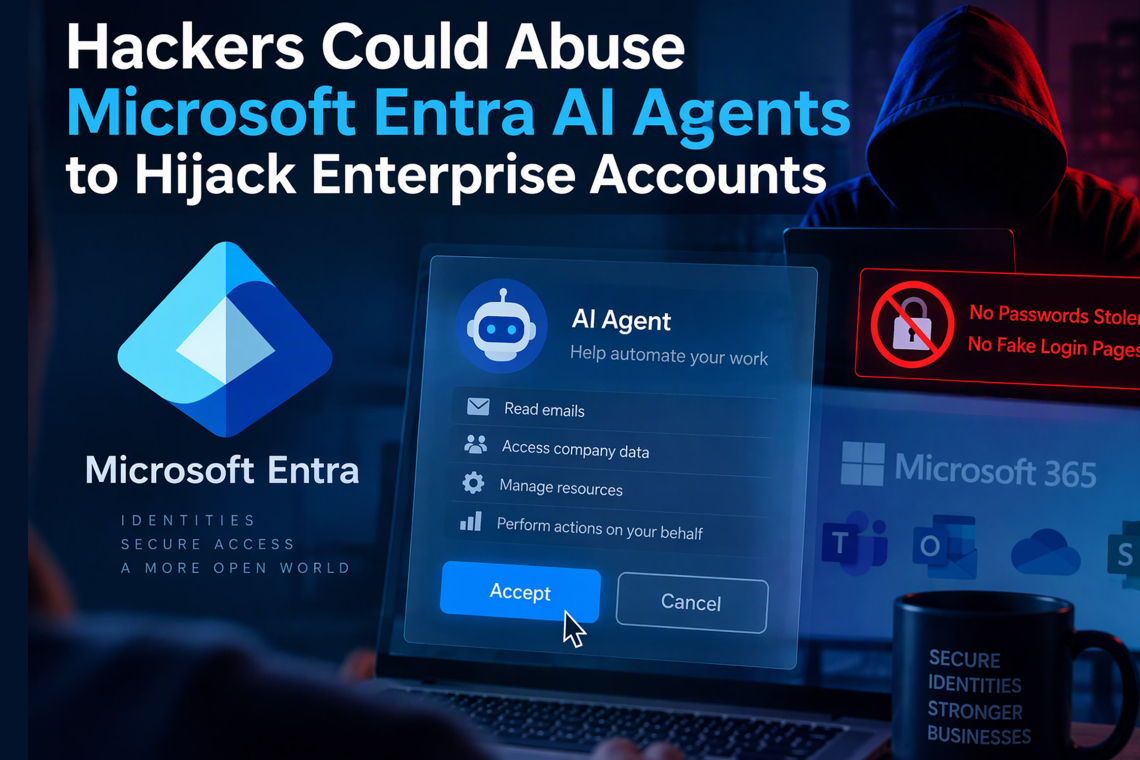
Security researchers have demonstrated a novel attack technique that allows threat actors to gain access to portions of a Microsoft 365 environment without stealing credentials, bypassing multifactor authentication, or deploying fake login pages. Instead, the attack relies on deceiving a user into authorizing a malicious AI agent, effectively granting attackers a foothold inside an organization's cloud environment.
Dubbed BluePhishing, the technique targets Microsoft Entra Agent ID, a framework that enables AI agents to possess their own identities within a Microsoft Entra tenant. By abusing the trust model behind these AI-powered identities, attackers can establish persistent access through legitimate authorization mechanisms rather than traditional credential theft.
The attack concept builds upon a familiar threat known as OAuth consent phishing, where victims unknowingly grant excessive permissions to malicious applications by accepting consent prompts. BluePhishing adapts this proven tactic to Microsoft's emerging AI agent ecosystem, where security awareness is still developing and administrative controls remain less mature.
The risk may increase in the near future as Microsoft expands access to Agent ID capabilities. According to Microsoft 365 Message Center notification MC1506733, standard Entra users are expected to receive the ability to create agent blueprints by default beginning in November 2026. Expanding blueprint creation privileges could significantly increase opportunities for unauthorized or malicious agent deployments within enterprise tenants.
Researchers from Proofpoint disclosed the BluePhishing technique in a report published on November 9, 2026. The cybersecurity company emphasized that the attack currently remains a proof-of-concept and that there is no evidence of active exploitation in the wild. Proofpoint also stated that Microsoft was notified of the findings prior to public disclosure.
How the BluePhishing Attack Works
Microsoft Entra Agent ID introduces a new identity model for AI agents that closely mirrors the architecture used by traditional enterprise applications.
At the core of the system is the agent blueprint, which functions similarly to an application registration. Each blueprint can be instantiated within individual Microsoft 365 tenants as a blueprint principal, while operational AI agents known as agent identities are created from these blueprints and perform actions on behalf of users or organizations.
According to the researchers, a single blueprint can generate as many as 250 agent identities, dramatically expanding the potential impact of a successful compromise.
The attack begins when an adversary creates a malicious blueprint inside a tenant they control. The attacker then configures a client secret and sets the blueprint to support authentication from external organizations. While this configuration is not exposed through the standard Entra administrative portal, it can be enabled using PowerShell commands or the Microsoft Graph API.
The attacker also assigns broad Microsoft Graph permissions to the blueprint. Any agent identities created from that blueprint automatically inherit these privileges. The approach resembles previous OAuth abuse campaigns in which malicious Entra applications served as long-term persistence mechanisms, allowing attackers to retain access even after victims changed passwords or reset credentials.

Once the malicious setup is complete, the attacker distributes a specially crafted consent URL to the target. If the victim approves the request, a blueprint principal is automatically deployed into the organization's Entra tenant.
Researchers discovered that the newly created blueprint principal is automatically granted a permission called AgentIdentity.CreateAsManager, a privilege that cannot currently be removed. This permission becomes the foundation for the remainder of the attack chain.
Armed with the blueprint identifier, the associated secret, the victim organization's tenant ID, and the identity of a designated sponsor user, attackers can generate Microsoft Graph access tokens and create agent identities directly inside the victim's environment.
Importantly, none of these required details are considered highly protected secrets. Tenant IDs can often be obtained through publicly accessible Microsoft sign-in discovery mechanisms, while blueprint identifiers and secrets remain under the attacker's control.
During testing, researchers successfully created an agent identity with permissions such as User.Read.All and Group.Read.All, then leveraged the GraphRunner tool to execute Microsoft Graph queries and enumerate organizational data.
The severity of the attack increases substantially when administrative consent is granted. While standard user consent limits permissions to the affected user's delegated access, administrator approval can provide tenant-wide application permissions, potentially exposing an entire Microsoft 365 environment through a single authorization event.
Why BluePhishing Could Be Difficult to Detect
One of the most concerning aspects of BluePhishing is that malicious activity blends naturally into expected AI-agent behavior.
Unlike traditional malware or suspicious background applications, AI agents are specifically designed to operate autonomously. Their interactions with Microsoft Graph services, automated workflows, and ongoing cloud activity may appear completely legitimate to administrators monitoring the environment.
Proofpoint researchers also noted several visibility limitations within the current Entra Agent ID ecosystem. Permissions inherited by agent identities are not clearly displayed within the Entra administrative portal and are similarly absent from standard Microsoft Graph views. Instead, these inherited rights only become visible when authorization tokens are generated at runtime.
This visibility gap can complicate investigations and make it harder for defenders to understand the true capabilities of deployed agent identities.
The researchers further highlighted challenges associated with auditing agent activity. Previous investigations involving Entra Agent ID logging demonstrated that incident responders often need to correlate information across multiple logging sources to accurately reconstruct agent behaviors and privilege assignments.

The architecture itself can also magnify risk. Traditional Microsoft Entra application registrations typically correspond to a single service principal within a tenant, whereas one malicious blueprint can spawn hundreds of individual agent identities, dramatically increasing the attack surface and potential blast radius.
BluePhishing is not the first security concern surrounding Entra Agent ID. Earlier research from Silverfort uncovered weaknesses involving the Agent ID Administrator role, reinforcing concerns that Microsoft's rapidly evolving AI identity infrastructure remains in its early stages of security maturation.
Defensive Strategies for Organizations
To minimize exposure to BluePhishing-style attacks, security teams should extend existing OAuth security practices to AI agent environments.
Organizations should educate employees to carefully scrutinize permission requests from third-party AI agents and avoid approving access requests from unknown or unverified sources.
Security administrators should also enforce the same consent governance policies used for traditional OAuth applications across agent blueprints and agent identities. Restricting self-service consent and requiring administrative review for high-risk permissions can significantly reduce attack opportunities.
Microsoft already blocks certain dangerous Microsoft Graph permissions, including User.ReadWrite.All, from being assigned to agents. Organizations should supplement these protections by implementing permission classifications, enforcing least-privilege access principles, and applying Conditional Access policies specifically designed for agent identities.
Additional safeguards include deploying Microsoft Entra ID Protection to monitor anomalous behavior and continuously evaluate identity-related risks.
Security teams should also monitor audit logs for key lifecycle events. Administrators can identify blueprint deployments through "Add application" audit events and detect agent identity creation through "Add service principal" records. Continuous monitoring of these events can provide valuable early-warning indicators of unauthorized activity.
The emergence of BluePhishing follows other AI-themed social engineering techniques that have already proven effective. One example, known as CoPhish Copilot Studio, leveraged a trusted Microsoft-hosted agent to trick users into granting OAuth permissions. BluePhishing raises the stakes further by targeting the AI agent identity model itself, potentially making fraudulent authorization requests appear even more legitimate to unsuspecting users.
As enterprises accelerate AI adoption across Microsoft 365 environments, BluePhishing serves as a reminder that modern attackers are increasingly targeting identity systems and authorization workflows rather than passwords alone. The growing use of autonomous AI agents may introduce powerful productivity benefits, but it also creates a new category of identity-based risks that defenders must be prepared to address.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
