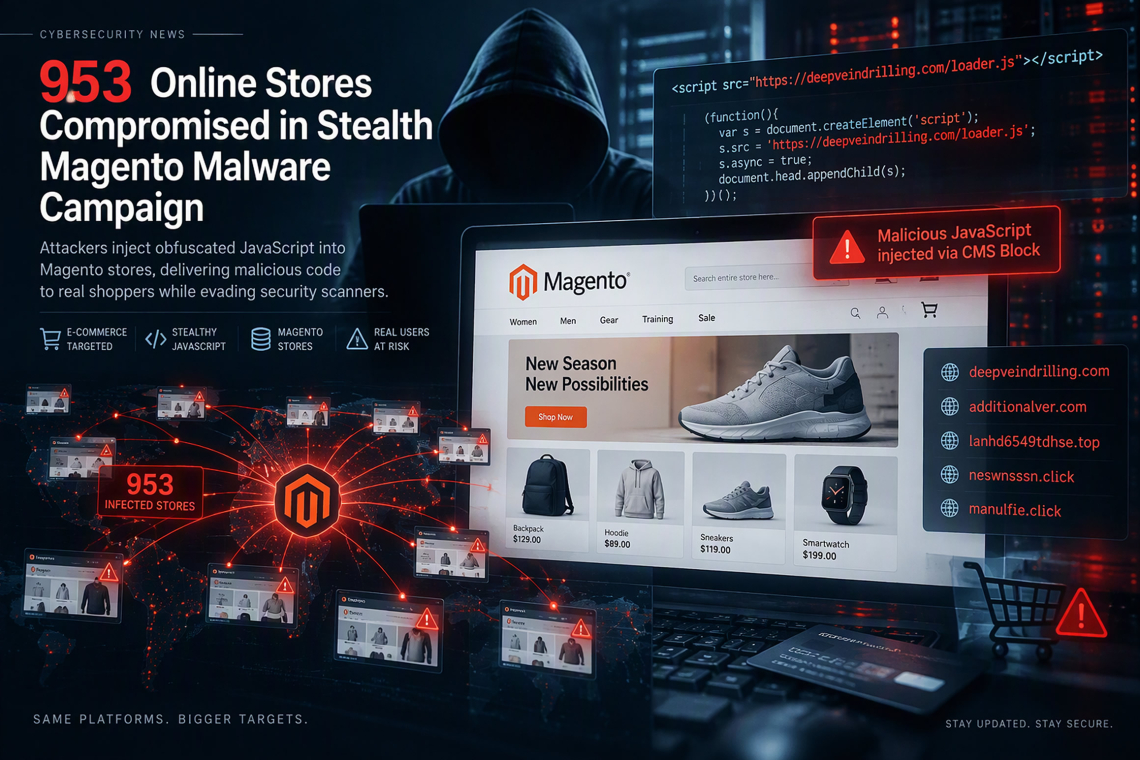
A sophisticated and still-unidentified threat actor has compromised 953 e-commerce websites, the majority of which are powered by Magento, in a malicious campaign that has been ongoing since July 2025.
Researchers at Dutch e-commerce security firm Sansec revealed that the attackers are embedding a small snippet of code into affected online stores. When visitors browse the compromised websites, the code silently triggers a malicious JavaScript loader delivered through Magento CMS blocks.
According to Sansec, the loader acts as a communication bridge between a visitor’s browser and attacker-controlled servers. Once activated, it first determines whether the visitor is a genuine shopper or an automated security scanner. If the request comes from a security tool, the server withholds any malicious response, allowing the operation to remain largely hidden from detection systems.
Over the course of the campaign, investigators have linked the activity to five different domains that have been rotated periodically:
- manulfie[.]click (July 2025)
- neswnsssn[.]click (December 2025)
- lanhd6549tdhse[.]top (March 2026)
- additionalver[.]com (June 2026)
- deepveindrilling[.]com (October 2026)
The newest domain, deepveindrilling[.]com, appeared in CMS blocks across at least 83 online stores shortly after its registration on October 6, 2026.
Researchers noted that the latest loader infrastructure is protected by Cloudflare and is designed to respond only to legitimate visitors of infected sites. The malicious code resides within Magento’s cms_block database table, a feature commonly used to display static content throughout online storefronts.
The attackers’ primary goal is to ensure their JavaScript payload executes automatically whenever an infected CMS block is rendered after a customer accesses the compromised website.
While it remains unclear whether the threat actor is altering existing CMS blocks such as headers, footers, and promotional banners or creating entirely new ones, either technique would effectively allow the malicious loader to execute.
Analysis uncovered two separate variants of the loader. The first downloads JavaScript from an attacker-controlled domain and stores the payload within the browser’s localStorage. This persistence mechanism allows the malware to continue functioning even if the external malicious domain is later taken offline.
A more advanced second version introduces browser fingerprinting capabilities. This enhancement enables the malware to identify and exclude bots, crawlers, and security analysis tools while selectively targeting real customers. Researchers have not yet determined the final payload delivered to victims.
Earlier stages of the operation relied on Keitaro, a traffic distribution and analytics platform often used to route web traffic dynamically. Through Keitaro, attackers could decide whether visitors received a malicious payload, were redirected elsewhere, or received no response at all, depending on their profile and browsing characteristics.
For example, requests to additionalver[.]com originating from Windows desktop systems returned a simple response that created a tracking cookie lasting 24 hours without delivering any obvious malicious content. The newer deepveindrilling[.]com infrastructure eliminates the dependency on Keitaro by incorporating visitor filtering and anti-bot functionality directly within the loader itself.
Regarding the initial compromise, Sansec estimates that 471 Magento stores were infected via the PolyShell (CVE-2026-48356) vulnerability. An additional 102 stores experienced malicious file uploads through exploitation of either PolyShell or SessionReaper (CVE-2025-54236).
In one investigated incident involving Magento 2.4.7-p1, researchers discovered PolyShell web shells disguised as PNG image files within the pub/media/custom_options/quote/ directory. The same store also contained references to the additionalver[.]com loader embedded in a CMS block. On October 7, the loader was updated to use deepveindrilling[.]com. The affected retailer had not yet installed Adobe’s APSB26-73 security update that addresses the PolyShell vulnerability.
Another compromise involved a store running Magento 2.4.7-p10 that had all core security patches applied. In that case, attackers reportedly gained access by creating an unauthorized administrator account and then using those elevated privileges to inject the malicious JavaScript.
To mitigate the threat, website owners are encouraged to perform comprehensive audits of administrator accounts, investigate unfamiliar CMS blocks, and review entries within the cms_block and cms_page database tables. Organizations should also maintain current security updates and implement strong authentication practices to reduce the risk of unauthorized access.
The findings emerge amid heightened concern over PHP2Shell, a pair of critical PHP vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619. Since their recent disclosure, the flaws have attracted widespread exploitation attempts from threat actors seeking to compromise vulnerable systems.
Adding to those concerns, Perplexity researcher Adel Karimi has documented what appears to be the first successful real-world exploitation of the PHP2Shell vulnerabilities. In observed attacks against honeypot servers, adversaries executed shell commands using utilities such as wget, curl, and the PHP command-line interface to retrieve additional payloads from the remote address 162.35.99[.]94:80. Although follow-on malware downloads have not yet been recovered, the activity demonstrates that active exploitation is already underway.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
