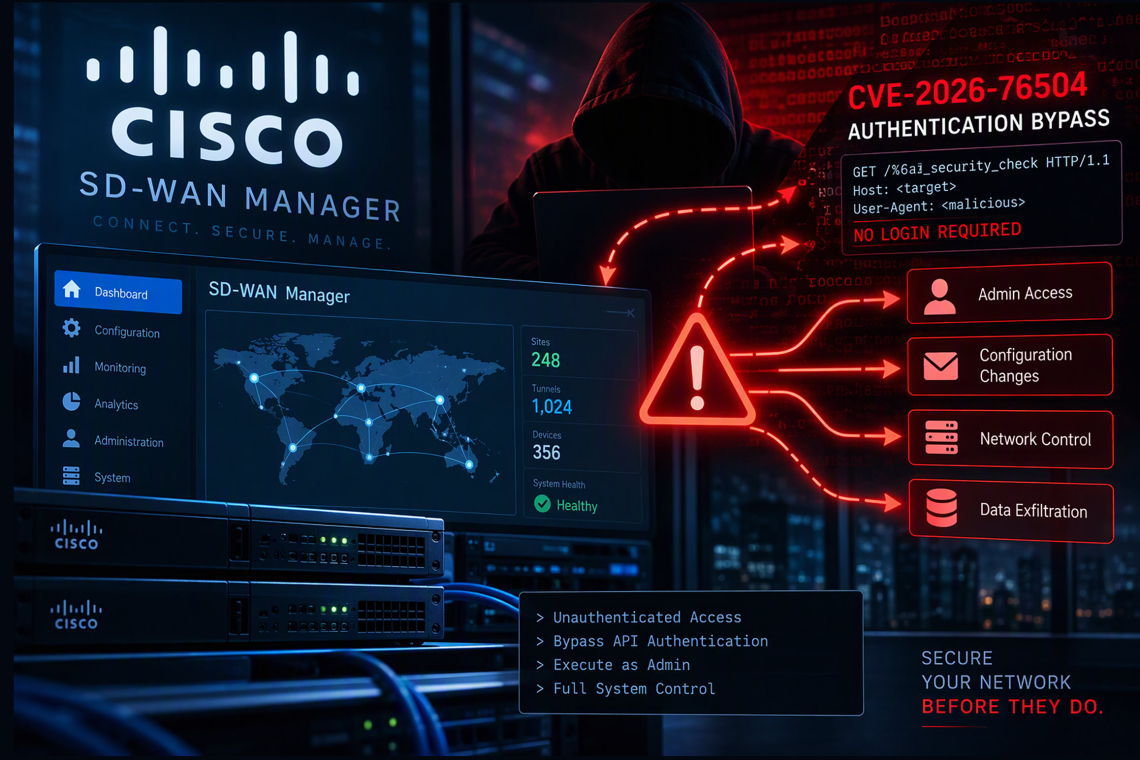
Cisco has alerted customers to the active exploitation of a newly disclosed critical zero-day vulnerability affecting Cisco Catalyst SD-WAN Manager, the centralized platform used to administer and monitor Cisco SD-WAN environments.
Tracked as CVE-2026-76504, the vulnerability carries a CVSS score of 9.8 and could enable a remote, unauthenticated attacker to gain administrator-level access through the SD-WAN Manager API. Cisco has released security updates to address the issue and emphasized that no workaround is currently available.
The flaw resides within the authentication component responsible for handling login sessions. According to Cisco, improper processing of URI-encoded HTTP requests allows a specially crafted request to bypass authentication controls protecting a specific API endpoint.
As a result, an attacker does not need valid credentials to exploit the vulnerability. Simply being able to send malicious requests to the SD-WAN Manager API may be enough to obtain administrative access. Systems exposed directly to the internet face the greatest risk, particularly because the default administrator account is assigned the netadmin role, which provides full administrative control over the platform.
Cisco's Product Security Incident Response Team (PSIRT) said it became aware of active exploitation of CVE-2026-76504 during September 2026. The vulnerability was identified while Cisco's Technical Assistance Center (TAC) was investigating a customer support case.
The company has not disclosed details regarding the number of affected organizations, the timing of the attacks, the threat actors involved, or the actions performed after successful exploitation.
Affected Deployments and Required Updates
Cisco confirmed that the vulnerability affects Catalyst SD-WAN Manager regardless of deployment configuration. No other Cisco products have been identified as vulnerable.
Organizations that previously installed updates for earlier SD-WAN vulnerabilities, including CVE-2026-20182, CVE-2026-20245, and CVE-2026-20262, must still apply the newly released patches because the fixes for CVE-2026-76504 are included in newer software versions.
Notably, some software release trains and deployment variants referenced in earlier advisories are absent from the latest guidance, including several 20.x versions as well as SD-WAN Cloud-Pro and SD-WAN for Government (FedRAMP) environments.
Cisco stated that Cisco SD-WAN Cloud (Cisco Managed) customers are already protected through software version 20.15.605 and do not need to take additional action.
For on-premises deployments awaiting upgrades, Cisco recommends limiting access to management interfaces from untrusted networks, especially the public internet. Where remote access is required, only trusted hosts should be permitted, and management services should be shielded behind firewalls and other network security controls.
Mitigation Recommendations
Until patches can be deployed, Cisco advises organizations to:
- Restrict SD-WAN Manager access from internet-facing networks.
- Allow administrative access only from trusted systems.
- Place management infrastructure behind firewalls.
- Use jump hosts or dedicated management networks for administration.
- Prevent direct exposure of administrative ports such as 443, 22, and 830.
Cisco also noted that Catalyst SD-WAN Cloud Hosted environments already implement protections that reduce exposure to this attack vector.
Detecting Potential Exploitation
Cisco's investigation revealed that exploitation attempts involve manipulation of the j_security_check login endpoint used for session-based authentication.
One observed example involves URI-encoding a character within the path:
In this case, %6a represents the letter j, allowing the request to bypass authentication restrictions.
Administrators are encouraged to review the following log files for suspicious requests originating from unknown IP addresses:
These accounts are reserved for internal service operations and may indicate unauthorized activity when appearing under unusual circumstances.
Cisco cautions that attackers may encode any character in the request path, meaning defenders should not limit hunting efforts to the %6a example alone. Because similar entries can appear during legitimate operations, each alert should be validated carefully to avoid false positives.
Incident Response Guidance
Organizations that suspect compromise should open a Severity 3 support case with Cisco TAC and reference CVE-2026-76504 in the case title. Cisco recommends generating an admin-tech diagnostic package before applying updates so investigators can examine the system for evidence of unauthorized access.
The advisory does not provide detection signatures or confirm whether patching alone will remove attackers who have already established persistence. Previous Cisco advisories addressing exploited SD-WAN vulnerabilities warned that software upgrades do not automatically remediate systems that have already been compromised.
Growing Threat to SD-WAN Infrastructure
CVE-2026-76504 is the latest in a string of heavily targeted Cisco SD-WAN vulnerabilities disclosed this year. By September 30, 2026, the U.S. Cybersecurity and Infrastructure Security Agency's Known Exploited Vulnerabilities (KEV) catalog included eight Cisco SD-WAN-related flaws added during 2026.
The active exploitation of this authentication bypass vulnerability underscores the continued interest of threat actors in enterprise network management platforms. Organizations operating Cisco SD-WAN environments should prioritize patching, restrict exposure of management interfaces, and closely monitor logs for indicators of unauthorized access.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
